


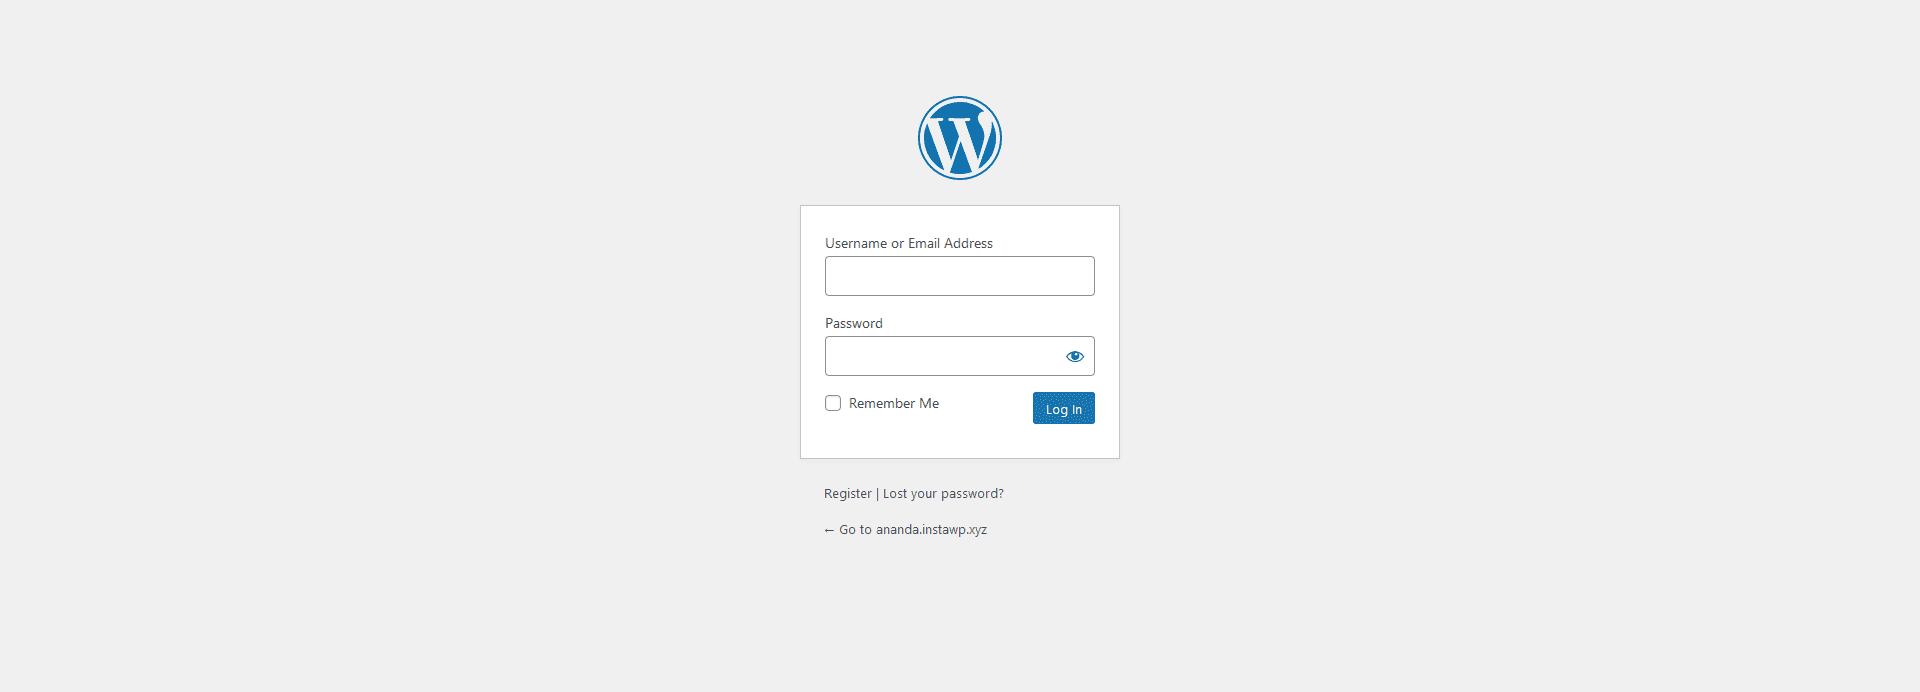
The default WordPress login screen works fine, but it also says “default WordPress site” to anyone who sees it, including clients logging into a site you built for them. Branding it is a small change with an outsized effect on how finished a client site feels — and the security half of this page (changing the login URL, adding two-factor) is worth understanding on its own terms, not as an afterthought bundled in with the visual work.
What’s Actually Worth Customizing
- The logo — swap WordPress’s own logo for yours or your client’s; this is the single highest-impact, lowest-effort change.
- Background and form colors — match the login screen to the site’s brand rather than WordPress’s default gray-on-white.
- The logo’s link destination — by default it links to WordPress.org; point it at your own site instead.
- The login URL itself — a separate concern from branding, this is a security measure (changing away from the default
/wp-login.php) rather than a cosmetic one, and worth doing independently of visual branding.

Three Ways to Do It
1. A dedicated login-customizer plugin
The fastest route for a one-off site: a plugin built specifically for this gives you a visual editor for the logo, colors, and background image without touching code. The tradeoff is one more active plugin for a feature that’s fundamentally simple.
2. A few lines of custom CSS via a filter
WordPress exposes a login_enqueue_scripts hook specifically for adding custom CSS to the login screen, without a dedicated plugin:
function custom_login_styles() {
    ?>
    <style>
        body.login {
            background-color: #f4f2ff;
        }
        .login h1 a {
            background-image: url(https://yoursite.com/wp-content/uploads/your-logo.png);
            background-size: contain;
            width: 240px;
            height: 80px;
        }
        .login #backtoblog a, .login #nav a {
            color: #4b3fbf;
        }
    </style>
    <?php
}
add_action('login_enqueue_scripts', 'custom_login_styles');

function custom_login_logo_url() {
    return home_url();
}
add_filter('login_headerurl', 'custom_login_logo_url');
Add this to a theme’s functions.php or, better for portability across theme changes, a small site-specific plugin. This is the leaner option if you’re comfortable with a few lines of PHP, and it avoids adding a whole plugin for what’s typically under 20 lines of CSS.
3. A theme or extension with login-page branding built in
Some all-in-one WordPress extensions bundle login-page branding alongside other admin customization (white-labeling, admin menu organization), so it’s a setting rather than a separate plugin decision if you’re already running one for other reasons.
Also Read: Nexter’s Unified Dashboard: A Complete Walkthrough of the New Admin Experience — for the broader admin-branding picture beyond just the login screen.
Why Login Attacks on WordPress Are So Relentless
The default login URLs (/wp-login.php and /wp-admin) are known to every attacker, because every WordPress site uses them by default. This isn’t a niche threat: large-scale, distributed brute-force campaigns against wp-login.php have been running continuously since at least 2013, and current attacks typically run from botnets of tens of thousands of compromised devices, each making a slow trickle of login attempts (often just one or two a minute per device) spread across a huge range of IP addresses specifically to stay under simple rate-limiting thresholds. A script hitting millions of WordPress domains simultaneously at their default login path doesn’t need to be sophisticated to be a real, ongoing cost — it just needs the URL to be predictable, which by default, it always is.
Is Hiding the Login URL “Real” Security, or Just Obscurity?
This is a genuinely debated point worth understanding both sides of, rather than treating as settled either way. The traditional security-industry objection is fair: changing the login URL is security through obscurity, it doesn’t fix a weak password, and it does nothing against an attacker who already specifically knows (or discovers) the custom URL. But the more practical framing, and the one worth actually acting on, is that changing the login path functions as attack-surface reduction, the same principle behind closing unused network ports — it isn’t a complete defense on its own, but it does eliminate the overwhelming majority of untargeted, automated bot traffic that only ever probes the default path and moves on when it hits a 404. The honest, balanced conclusion: hiding the URL is a real, low-cost win against commodity automated attacks, but it only becomes meaningful security when paired with rate limiting, a strong unique password, and two-factor authentication — not as a substitute for any of them.
A Worked Example: Branding an Agency Client Handoff
Take a realistic scenario: an agency finishes a client site build and needs to hand over admin access. The client will log in occasionally to review content, so first impressions on that login screen matter more than they might for a site the client never sees behind the scenes. The agency adds the client’s logo and brand colors via the CSS-hook method (avoiding a dedicated plugin for a one-time task), points the logo link at the client’s own homepage instead of WordPress.org, and separately — as a distinct step, not bundled into the branding work — changes the login URL away from the default and enables two-factor authentication on every admin account before handoff. The client experiences this as “a polished, professional login screen”; the agency knows the actual security posture improvement came from the second, invisible half of the work, not the logo.
Troubleshooting Common Login-Branding Issues
- The custom CSS doesn’t apply at all: confirm the
login_enqueue_scriptshook is firing — a typo in the function name passed toadd_action, or code placed in a file that isn’t actually loading, are the most common causes. - The logo shows but is the wrong size or blurry: check the background-image dimensions against the actual logo file’s resolution; a logo sized for a much larger context can render blurry when scaled down via CSS
background-size. - The branding disappears after a theme change: this happens when the code lives in the old theme’s
functions.phprather than a site-specific plugin — moving it to a small standalone plugin fixes this permanently. - Changed the login URL but forgot to bookmark or document it: a genuinely common and locking-yourself-out mistake — document the new URL somewhere durable (a password manager note, not just memory) before changing it, especially on a site with multiple admins.
Don’t Skip the Security Half of This
Visual branding and login security are separate concerns, but they’re often done at the same time. Changing the default login URL and adding two-factor authentication address a different problem (automated login attacks against a known, predictable URL) than a custom logo does, and neither substitutes for the other. Two-factor specifically closes the gap that a strong password alone doesn’t: even a correctly guessed or leaked password isn’t enough to log in without the second factor, which matters most for any account with publish or admin-level access.
Also Read: WordPress Cron Jobs Explained: How Scheduled Tasks Actually Work — another admin-side WordPress fundamental worth understanding alongside login security.
A Realistic Login-Hardening Checklist
- Change the login URL away from the default — cheap, eliminates most automated bot noise, not a complete defense on its own.
- Enable two-factor authentication, at minimum for every admin and publish-level account — this is the change that stops a leaked or guessed password from actually being usable.
- Use a genuinely unique, strong password per site, not a variation of one reused across accounts — a password manager makes this practical rather than aspirational.
- Add login rate limiting (via a security plugin, host-level protection, or a WAF), which catches the smaller number of attempts that do land on whatever your actual login path is.
- Brand the visual login screen last, once the above is in place — it’s the part clients see, but it isn’t the part doing the security work.
FAQ
Does customizing the login page make my site less secure?
No, visual branding alone doesn’t affect security either way. Changing the login URL is a separate, genuine security measure worth doing independently.
Do I need a plugin, or can I do this with just CSS?
Just CSS works fine for logo and color changes via the login_enqueue_scripts hook; a plugin mainly buys you a visual editor instead of writing the CSS yourself.
Will this survive a WordPress core update?
Yes, as long as it’s implemented through the standard hooks (login_enqueue_scripts, login_headerurl) rather than editing core files directly, which you should never do regardless.
Should this custom code go in functions.php or a separate plugin?
A small site-specific plugin is generally safer for portability: it survives a theme switch, whereas code in functions.php is lost the moment the active theme changes.
Is changing the login URL actually worth doing, or is it just security theater?
It’s genuinely worth doing, but as attack-surface reduction rather than a complete defense. It eliminates most untargeted automated bot attacks that only ever probe the default path, while doing nothing against an attacker who specifically knows or discovers the custom URL — pair it with two-factor authentication and rate limiting rather than relying on it alone.
How common are automated attacks against wp-login.php really?
Very common and ongoing rather than occasional — large-scale distributed brute-force campaigns against the default WordPress login path have been documented since 2013 and continue today, often run from botnets of tens of thousands of devices making slow, distributed attempts to avoid simple rate limits.
I changed the login URL and now I can’t log in — what do I do?
If a plugin made the change, most login-URL plugins can be reset via FTP/file access by renaming or removing the plugin’s folder, which typically restores the default login path. If the change was made via custom code, removing or commenting out that code the same way restores default behavior. This is exactly why documenting the new URL before changing it matters.
Is a password manager actually necessary for this, or is a strong memorized password enough?
A password manager makes genuinely unique, strong passwords per site practical rather than aspirational — the real risk isn’t a weak password on one site, it’s the same password reused across multiple sites, where a breach anywhere exposes every site that shares it. Two-factor authentication is still worth adding on top, since it protects even a strong password if it’s ever leaked some other way.
Conclusion
Branding and security are two separate jobs that happen to live on the same screen — do both, but don’t mistake one for the other. A custom logo makes the login page feel finished; changing the login URL, adding rate limiting, and turning on two-factor authentication are what actually make it safer, and none of them are optional just because the visual work is done.
Suggested Reading
- Nexter’s Unified Dashboard: A Complete Walkthrough of the New Admin Experience
- WordPress Cron Jobs Explained: How Scheduled Tasks Actually Work
- WordPress Dark Mode: How to Add a Site-Wide Light/Dark Toggle
