


Most WordPress break-ins are not clever. They are a bot working through a list of common usernames and passwords against your login page, thousands of times a day, until one combination sticks. You will not see it happen in real time unless something on your site is actually watching for it, and by default, WordPress core is not watching for it at all.
Nexter Extension closes that gap with two free, connected security modules: Limit Login Attempts, which blocks an IP address after repeated failed logins and keeps a log of every attempt, and Login Email Notification, which alerts you the moment someone actually gets in. Together they cover both sides of login security: stopping the guessing, and knowing about it when a login succeeds. Here is how to set both up properly.

Why Login Security Needs More Than a Strong Password
A strong password helps, but it does not stop a brute-force script from trying anyway, and it does nothing to tell you when someone succeeds. Two separate problems sit under “login security”: keeping automated attackers out, and knowing what actually happened at your login page. A password manager solves neither on its own. That is the gap Nexter Extension’s Security tab is built to close, and it does it with two modules that work well together rather than one bolted-on feature.
How These Attacks Actually Happen
Brute-force login attacks on WordPress rarely involve a person sitting at a keyboard guessing passwords one at a time. They run as automated scripts that cycle through lists of common usernames (admin, administrator, the site owner’s name) paired with leaked or commonly reused passwords, hitting /wp-login.php hundreds or thousands of times in a session. Most of these scripts do not care which site they are attacking. They are pointed at wide ranges of WordPress installs and simply try the same playbook everywhere, which is exactly why a generic, unmonitored login page is a soft target even on a small site with no obvious reason to be attacked.
The two failure modes that follow from this are different, and worth separating. The first is the attack itself succeeding, where a weak or reused password finally matches and someone gets in. The second, less obvious one is the attack quietly consuming server resources, since thousands of failed login requests still load PHP, query the database, and can slow a site down or trip a host’s resource limits, even when every single attempt fails. A login limiter addresses both: it blocks the IP before the password guessing gets anywhere, and it stops burning server resources on a script that would otherwise keep hammering the login form indefinitely.
What Limit Login Attempts Actually Does
Limit Login Attempts is a freemium module inside Nexter Extension that tracks failed login tries by IP address and temporarily blocks an address once it crosses a threshold you set. The free version already includes the part most competing plugins charge for: a running log of every blocked attempt, viewable from inside the settings popup.
Also Read: How to Add Two-Factor Authentication to WordPress for a second layer of protection on top of login-attempt limits.
Setting Up Limit Login Attempts, Step by Step
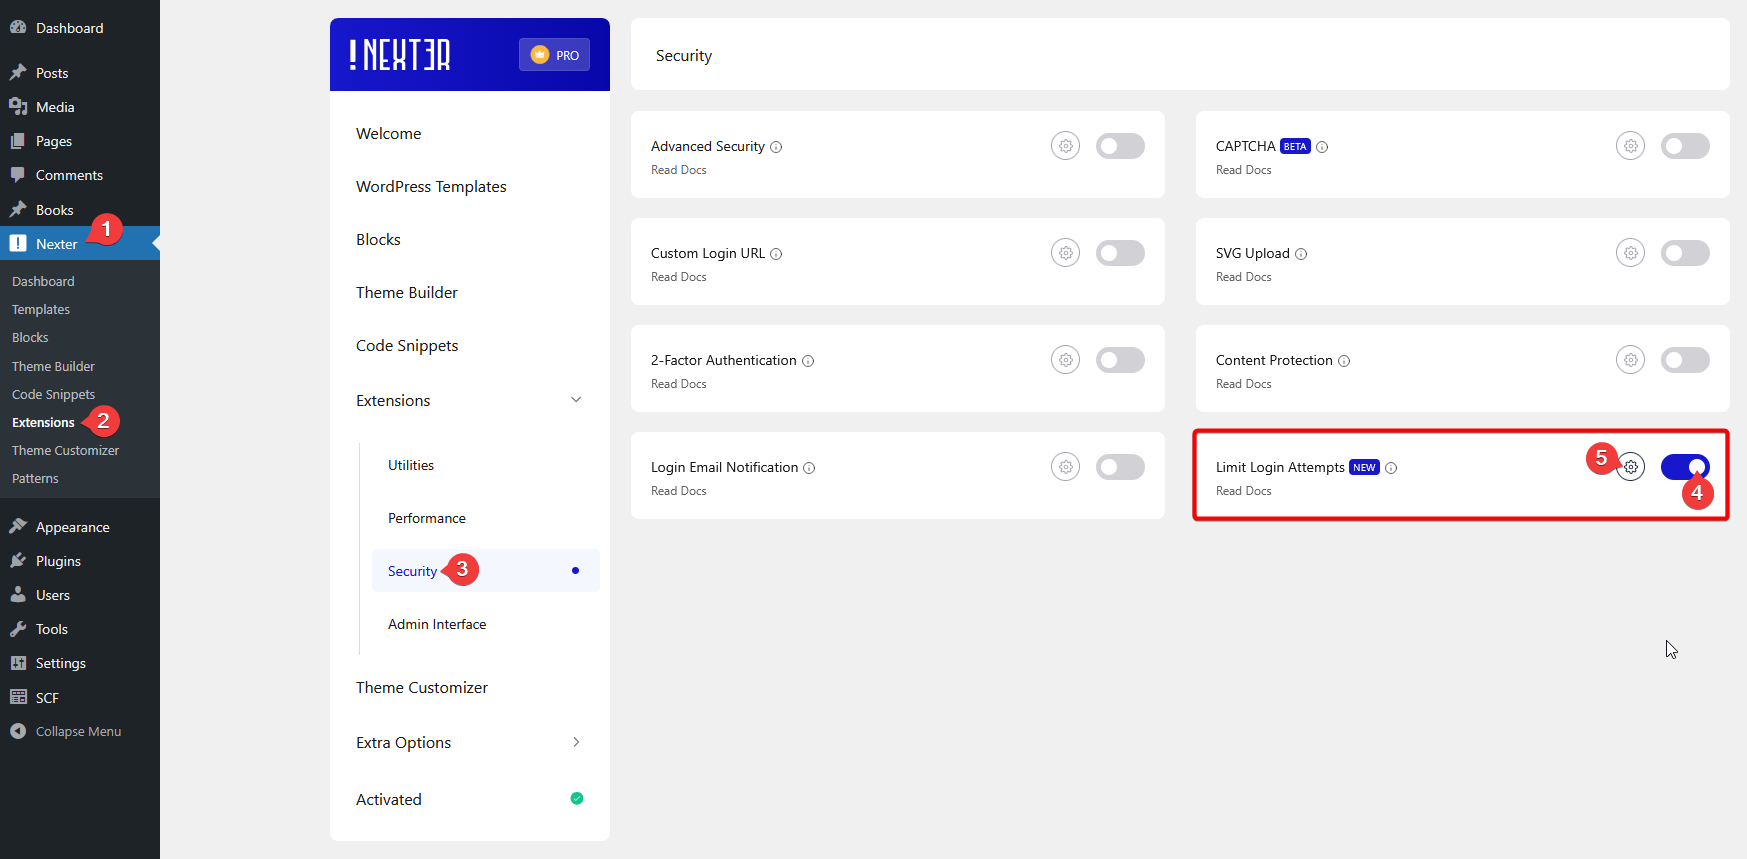
From the WordPress dashboard, go to Nexter > Extensions > Security, find the Limit Login Attempts section, and switch it on. Click the gear icon next to it to open the settings popup.
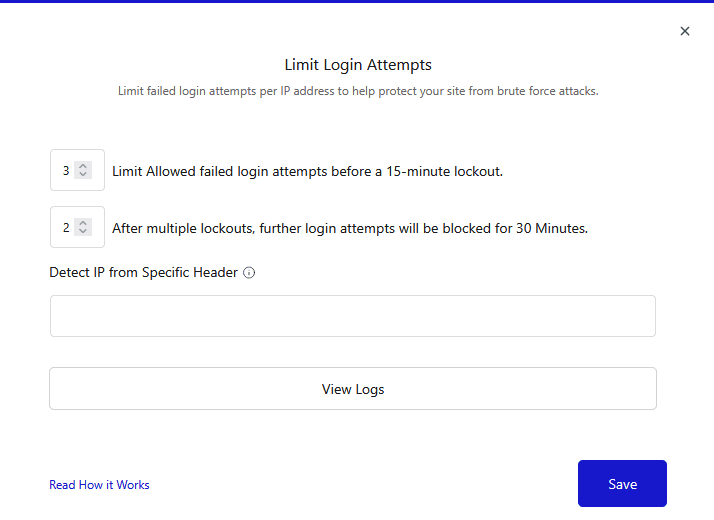
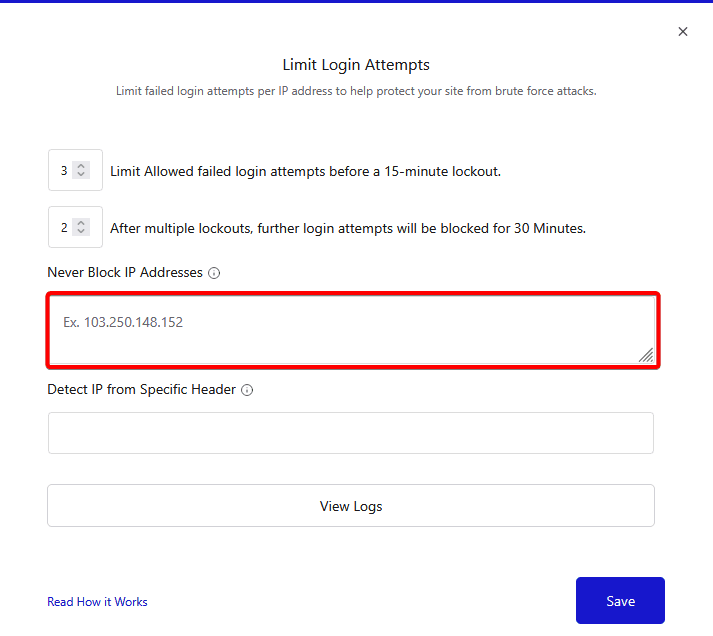
The popup has a handful of fields, and each one matters more than it looks:
- Failed attempts before block. Set how many consecutive wrong passwords trigger a 15-minute block on that IP address. A value of 3 to 5 is a reasonable starting point; too low and a forgetful team member locks themselves out over a typo.
- Repeat-offense escalation. Set how many times the same IP can hit a 15-minute block before the penalty jumps to 30 minutes. A value of 2 means a second 15-minute block in a row upgrades the next one automatically, which punishes a script that keeps retrying without punishing a one-off mistake.
- Detect IP from Specific Header. If your site sits behind Cloudflare, Sucuri, or your host’s load balancer, your server sees the proxy’s IP address instead of the real visitor’s. Add
HTTP_X_FORWARDED_FORin this field so the plugin reads the actual visitor IP from the forwarded header instead of blocking your proxy by mistake. Leave it blank if you are not behind a proxy. - View Logs. This button opens the record of every blocked attempt: the IP address, the timestamp, and the username that was tried. It is the closest thing to an activity log for your login page, and it is where you would check first if you suspected a targeted attack rather than routine bot noise.
Save the settings, and the module starts enforcing them immediately. There is nothing else to configure on the free plan.
Excluding Trusted IP Addresses (Nexter Extension Pro)
The one real risk with any login limiter is locking out someone who should not be locked out, usually a developer testing on a shared connection or a client who fat-fingers their password twice before coffee. Nexter Extension Pro adds a Never Block IP Addresses field inside the same popup, where you can list trusted IPs, one per line, that stay exempt no matter how many failed attempts come from them.
This matters more on agency and client sites than on a single blog, since the person you least want locked out during a launch week is whoever is actually building the site.
Adding Login Email Notifications for Real-Time Alerts
Limiting failed attempts stops guessing. It does not tell you when a login actually succeeds, which matters just as much, since a successful login from an unfamiliar location is often the first sign something is wrong. Nexter Extension’s Login Email Notification module, also under Nexter > Extensions > Security, sends a custom email the moment anyone logs in.

Enable the toggle, click the gear icon, and configure four fields: Who Get Alert (pick which user roles trigger a notification, so you are not emailed every time a subscriber logs in), Exclude IPs (a comma-separated list of addresses that should not trigger an alert, useful for your own office or home IP), and a custom Subject and Message for the email itself. Save it, and every future login from a covered role sends the alert automatically.
Also Read: How to Change the WordPress Login URL to pair login alerts with a hidden admin URL for a much smaller attack surface.
What to Do If the Log Shows a Real Attack
Most of what shows up in View Logs is routine bot noise: a handful of blocked attempts from scattered IP addresses, none of which return. A real, targeted attack looks different, and it is worth knowing what that looks like before you see it. Watch for a high volume of attempts from the same IP or a narrow IP range, repeated attempts against a specific username rather than a random spread, or blocks that keep escalating from 15 minutes to 30 minutes over and over from the same source.
If you see that pattern, a few steps beyond the plugin’s own blocking are worth taking. Change the password on any account the attacker was actually targeting, even if the attempts all failed, since a targeted attempt sometimes means the username was leaked from elsewhere. Add the offending IP to a block list at the host or CDN level (Cloudflare, Sucuri, or your hosting provider’s firewall) for a more permanent block than the plugin’s own 15 or 30-minute window. And if the same pattern keeps recurring against your default login URL, that is a reasonable trigger to finally set up a custom login URL rather than treating it as optional.
Pairing Login Monitoring with the Rest of Nexter’s Security Toolkit
Limit Login Attempts and Login Email Notification are two modules inside a wider Nexter Extension security tab that also includes a Custom Login URL, reCAPTCHA or Cloudflare Turnstile on your forms, two-factor authentication on the Pro plan, and general hardening tweaks grouped under Advanced Security. None of these need a separate plugin, and none of them conflict with each other, since they are built to run together from the same Security tab rather than as isolated add-ons.
A reasonable baseline for most sites: turn on Limit Login Attempts with a moderate threshold, turn on Login Email Notification for administrators only, change your login URL, and add 2FA if you are on Pro. That combination covers brute force, unauthorized access, and silent account takeover without adding a separate security plugin to the stack.
Common Mistakes to Avoid
- Setting the failed-attempt threshold too low. A value of 1 or 2 locks out real users over routine typos. Give people room for an honest mistake.
- Forgetting the proxy header on a Cloudflare-protected site. Without
HTTP_X_FORWARDED_FORset correctly, the plugin may end up blocking your proxy’s shared IP instead of the actual attacker, which can lock out every visitor at once. - Sending login alerts for every user role. On a membership or course site with hundreds of subscribers, alerting on every login buries the one email that actually matters. Scope it to administrators and editors.
- Never checking the log. The View Logs button is only useful if someone actually looks at it occasionally. A five-minute check after a suspicious traffic spike is enough to catch a targeted attempt early.
- Treating login limits as a full security plan. They stop one attack vector. Pair them with a login URL change, form captchas, and regular core and plugin updates.
Frequently Asked Questions
Is Limit Login Attempts free in Nexter Extension?
Yes. The core Limit Login Attempts module, including the failed-attempt threshold, escalating lockout duration, and the login log, is included in the free Nexter Extension. The Pro version adds a Never Block IP Addresses allowlist on top of the same free-tier controls.
Where do I find the login attempt log?
Open the Limit Login Attempts settings popup under Nexter > Extensions > Security and click View Logs. It lists every blocked attempt with the IP address, timestamp, and username that was tried.
Can I get an email every time someone logs into my site?
Yes, through the separate Login Email Notification module in the same Security tab. You choose which user roles trigger an alert and can exclude specific IP addresses, so you are not emailed for your own routine logins.
Will Limit Login Attempts lock me out of my own site?
It can, if you set the threshold too low and mistype your password a few times. Setting a moderate threshold, such as 3 to 5 attempts, and using the Never Block IP Addresses field on Pro for your own connection avoids that.
Do I need a separate security plugin alongside Nexter Extension?
Not for login security specifically. Limit Login Attempts, Login Email Notification, Custom Login URL, reCAPTCHA, and two-factor authentication all live in the same Nexter Extension Security tab and are built to work together, which covers what most dedicated login-security plugins offer on their own.
What happens to a blocked IP address after the lockout period ends?
The block is temporary and lifts automatically once the 15 or 30-minute window passes, after which that IP can attempt to log in again. If it fails the threshold again, it gets blocked again, with the escalation counter continuing to climb. Nexter Extension Pro’s Never Block IP Addresses field is the way to permanently exempt an address instead of waiting out repeated temporary blocks.
